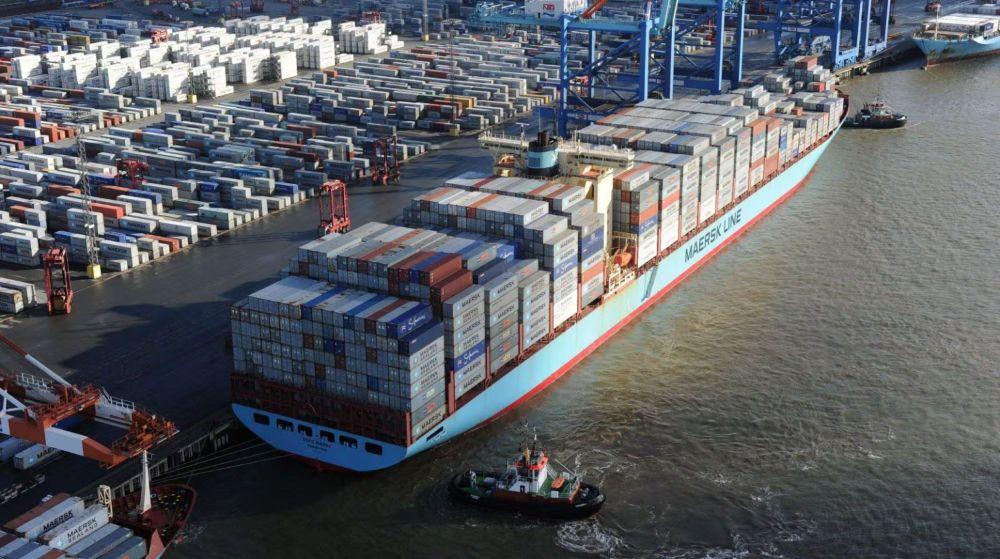
Danish shipping giant Maersk has verified a cyber intrusion in which attackers gained access to an older system and extracted data.
The Copenhagen-based group said on Wednesday that it is investigating an IT security incident involving unauthorised access and data extraction from one of its local legacy systems.
“We take cyber security and data protection very seriously and would like to keep our customers informed about the incident.” According to the carrier, the event concerned a local legacy system obtained via an earlier acquisition.
After spotting the intrusion, Maersk’s cybersecurity team began a full investigation and acted to secure the affected system.
The company stated that its findings so far strongly suggested that no sensitive data had been disclosed.
“The incident is isolated to a local system, and we have found no indication that there has been any impact on other Maersk systems or customer and partner systems that connect to Maersk through integrations such as APIs and EDI,” the company said.
The company emphasized that it does not expect disruption to customer operations at this time and that customers can continue to use Maersk platforms to book and manage their shipments as usual.
Maersk has not named the acquired business, disclosed what data was extracted, or identified those responsible for the data intrusion.
The carrier advised its customers to treat any unexpected communications claiming to relate to this matter with caution and verify them through their usual Maersk contact.
As investigation remains ongoing, Maersk emphasized that will keep its customers updated as more information becomes available and if it identifies any need to inform impacted parties of any further findings, it will do so.
The company also said it has rigorous processes in place to identify and prevent incidents and minimise customer impact, adding that cyber security remains a constant, ongoing priority for the Danish group.
Robban Assafina is now on WhatsApp channel. Click Here